
Responsible AI is changing.
For years, much of the discussion focused on principles.
Fairness.
Transparency.
Privacy.
Safety.
Accountability.
Those principles remain important.
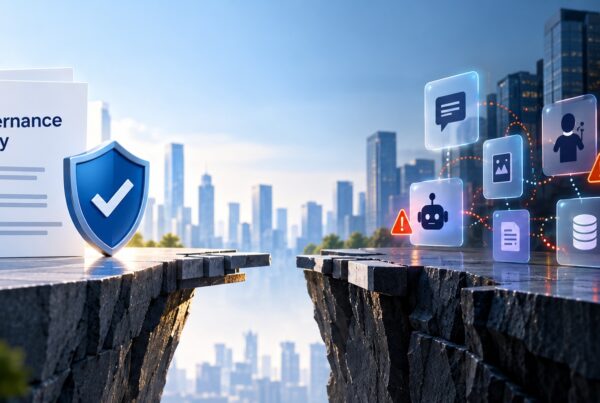
But as AI moves deeper into enterprise operations, principles alone are no longer enough.
Organizations increasingly need to know whether those principles are actually reflected in the AI systems, applications and agents operating inside the business.
Microsoft’s 2026 Responsible AI Transparency Report provides a useful view of this transition.
The report describes a responsible AI program that is becoming more adaptive, more closely integrated with engineering and more dependent on continuous evidence from real-world deployment.
That points to a broader shift in enterprise AI management.
Responsible AI is moving from policy toward continuous governance.
Responsible AI Can No Longer Be a Point-in-Time Exercise
Traditional governance processes often assume that technology can be reviewed before deployment, approved and then reassessed periodically.
That model becomes increasingly difficult as AI systems become dynamic.
Models change.
Applications introduce new AI capabilities.
Providers update services.
AI systems gain memory.
Agents gain access to additional tools.
Permissions evolve.
Usage patterns change.
New risks emerge through real-world interaction.
An assessment performed six months ago may therefore describe an AI environment that no longer exists.
Microsoft’s 2026 report explicitly describes responsible AI as a continuous discipline and highlights a shift away from release and point-in-time assessments toward ongoing governance.
This is one of the most important developments in enterprise AI governance.
The governance question is no longer simply:
Was this AI system approved?
It becomes:
Is this AI system still operating within the conditions under which it was approved?
Adaptive Governance Starts With Knowing What Exists
One of the less dramatic but most important themes in Microsoft’s report is inventory.
The re-engineered Responsible AI Standard distinguishes among AI models, platform services and applications and emphasizes the need to understand where AI technology exists and which risk requirements apply.
This matters because organizations cannot govern an AI environment they cannot describe.
Enterprise AI rarely arrives through one channel.
An organization may use:
enterprise AI applications,
embedded AI capabilities inside existing software,
developer AI tools,
external models accessed through APIs,
internally developed AI applications,
AI agents,
third-party agents,
and AI services adopted independently by employees.
The AI inventory therefore has to become broader than a procurement list.
It needs to answer:
What AI exists?
Which provider or model is involved?
Where is it being used?
Who owns it?
Who is using it?
What business process does it support?
Which data and systems can it access?
Which governance requirements apply?
Without that context, responsible AI remains disconnected from operational reality.
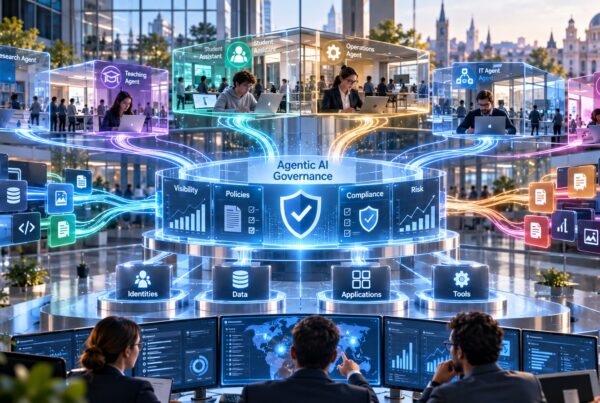
Agentic AI Changes the Unit of Governance
Microsoft’s report gives particular attention to agentic AI.
That is significant because agents change what governance needs to observe.
A traditional AI model primarily produces an output.
An agent may do much more.
It may retain memory.
It may choose a tool.
It may retrieve enterprise data.
It may call an API.
It may act on behalf of a user.
It may delegate part of a task.
It may interact with another agent.
It may execute a consequential action.
The governance boundary therefore expands beyond the model.
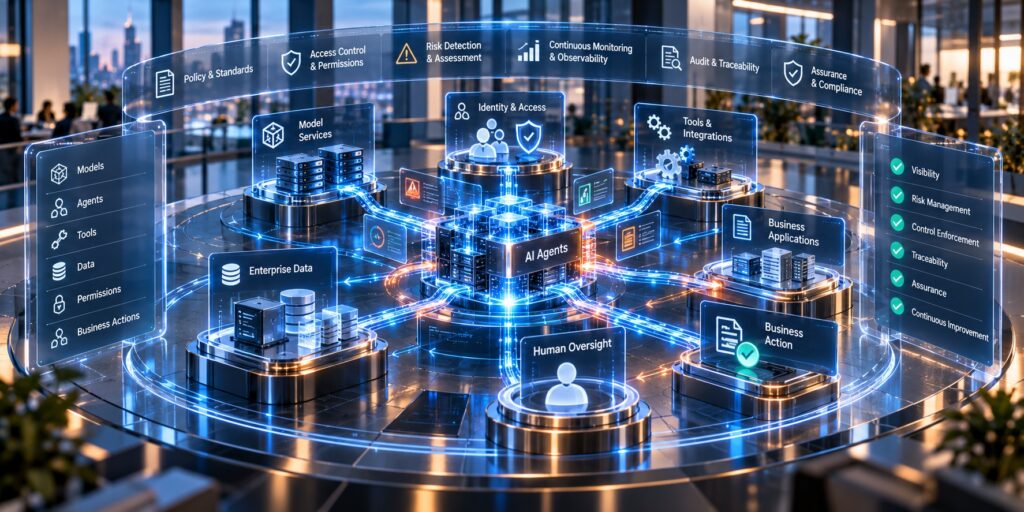
Organizations need to understand relationships among:
Agent
Identity
Model
Tool
Data
Application
Permission
Action
Human oversight
Business purpose
Microsoft’s investments in agent identity, runtime policies, evaluation and observability reflect this shift.
But the underlying management principle applies beyond any single technology ecosystem.
As AI becomes agentic, governance has to follow execution, not just configuration.
Responsible AI Governance Is Becoming Evidence-Based
A policy states what should happen.
Evidence helps determine what actually happened.
This distinction becomes increasingly important as governance moves into production environments.
Microsoft describes expanding logging, observability, evaluation, red teaming, runtime controls and post-release monitoring across its responsible AI program.
Those capabilities generate evidence.
Evidence that an assessment occurred.
Evidence that a policy was applied.
Evidence that an agent used a particular tool.
Evidence that an approval gate was triggered.
Evidence that a risk was identified.
Evidence that an issue was investigated.
Evidence that a mitigation remains effective.
This is what begins to turn responsible AI from a policy framework into an operating discipline.
It also changes the role of governance teams.
Instead of relying only on documentation created at deployment, they increasingly need access to current evidence from the systems themselves.
Continuous Evaluation Is Becoming Part of Assurance
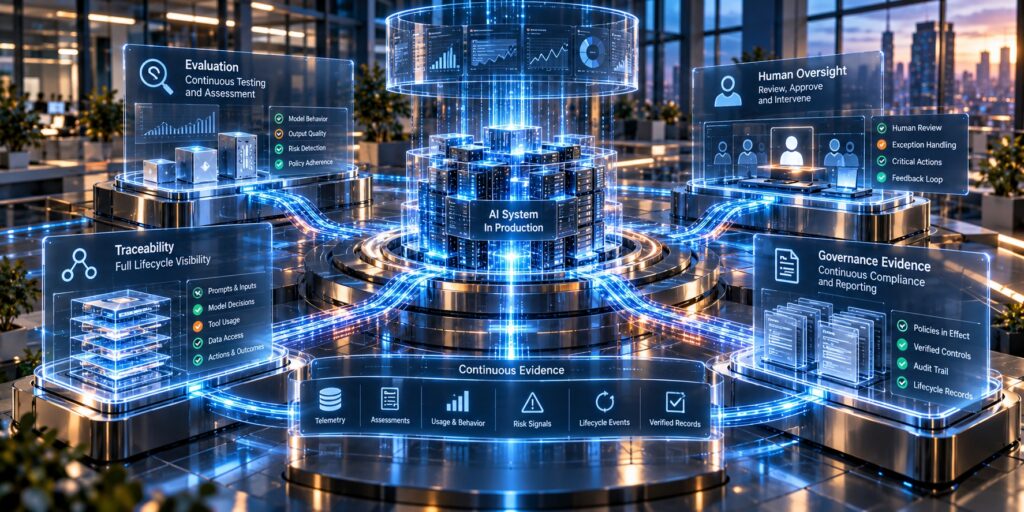
Another important theme in the report is evaluation.
AI systems are probabilistic.
Agentic systems add another layer of uncertainty because behavior can emerge across multiple steps, tools and external inputs.
Pre-deployment testing remains necessary.
But it cannot prove that an AI system will continue behaving exactly as expected after deployment.
This makes continuous evaluation increasingly important.
Organizations need to ask:
Is the system still performing as expected?
Are safeguards still effective?
Has behavior drifted?
Are agents remaining within task boundaries?
Is human intervention still available where required?
Can important actions still be traced?
This is where responsible AI begins to converge with AI assurance.
Assurance is not simply declaring that controls exist.
It requires evidence that expected controls, oversight and behavior can be demonstrated.
Human Oversight Still Matters as Autonomy Increases
More autonomous AI does not eliminate human accountability.
It makes the design of human oversight more important.
Microsoft’s report describes approval gates, intervention mechanisms and controls designed to preserve meaningful human oversight for consequential agent actions.
The enterprise question, however, is broader than whether a button exists.
Organizations need to understand:
Which decisions require human approval?
Who is responsible for that approval?
Can execution be interrupted?
What happens when no human is available?
Can the organization demonstrate that the expected oversight actually occurred?
Human oversight therefore becomes both a control and an assurance question.
Responsible Deployment Is Different From Responsible Development
Microsoft’s re-engineered Responsible AI Standard now explicitly distinguishes between developer and deployer responsibilities.
This distinction matters well beyond Microsoft.
Most enterprises are not developing every AI system they use.
They are deploying technology created by others.
An organization may purchase an AI application, integrate an external model, deploy a third-party agent or enable AI functionality inside an existing SaaS platform.
The developer is responsible for how the technology was built.
The enterprise deployer remains responsible for how that technology is used inside its own environment.
That includes questions such as:
Is the use case appropriate?
What organizational data is involved?
Who has access?
What safeguards are required?
How are users informed?
What monitoring is available?
What happens when an issue occurs?
What residual risk has the organization accepted?
This shared-responsibility model is critical for enterprise AI governance.
A provider’s responsible AI program does not remove the enterprise’s responsibility to govern its own deployment.
Standards Are Becoming Part of Operational AI Assurance
Microsoft’s report also highlights increasing alignment between responsible AI governance, standards and assurance.
ISO/IEC 42001 is particularly relevant.
It establishes an AI management system framework for organizations that develop, provide or use AI systems.
Microsoft reports ISO/IEC 42001 certification across a broad portfolio of AI systems and also describes participation in broader initiatives designed to improve assurance interoperability across the AI value chain.
This reflects an important shift in enterprise governance.
Standards should not exist separately from operational evidence.
Organizations increasingly need to understand:
Which requirements apply?
Which organizational capabilities support them?
What evidence demonstrates implementation?
Where are the gaps?
How current is the evidence?
A framework mapping without evidence is documentation.
A framework mapping connected to current operational evidence becomes much more useful for governance and assurance.
The Enterprise Problem Is Larger Than Any One Provider
Microsoft’s report shows how one major AI provider is evolving its own governance architecture.
But most enterprises do not operate inside one AI ecosystem.
They may use AI services from multiple providers.
They may have developer assistants from one vendor, foundation models from another, enterprise AI applications from several others and internally built agents operating across all of them.
Security evidence may come from different platforms.
Identity evidence may come from another system.
Work output may live in development, project or business applications.
Cost may be spread across licenses, APIs, tokens, cloud infrastructure and business-unit subscriptions.
This creates a management challenge above the provider layer.
Each provider can explain what happens inside its own environment.
The enterprise still needs to understand the combined AI environment.
Where AssetUno AI Fits
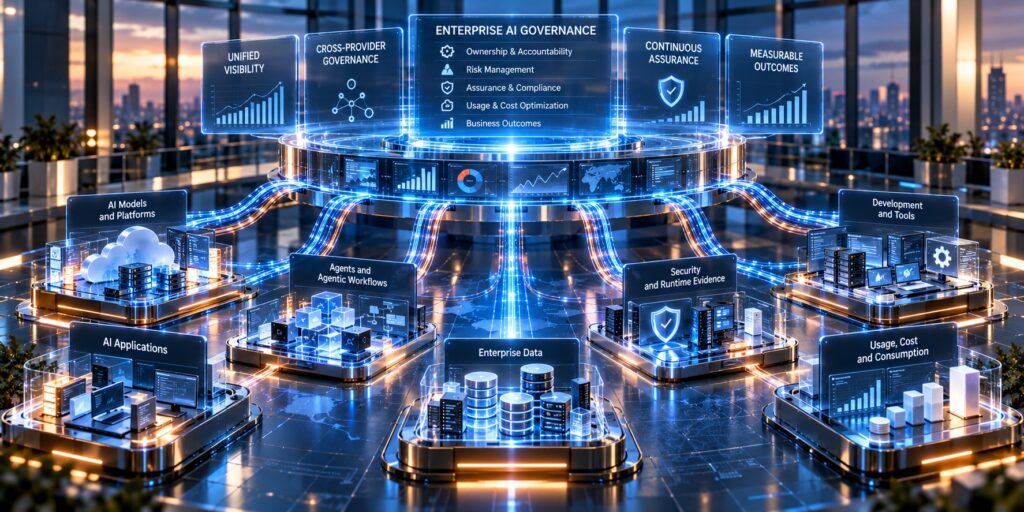
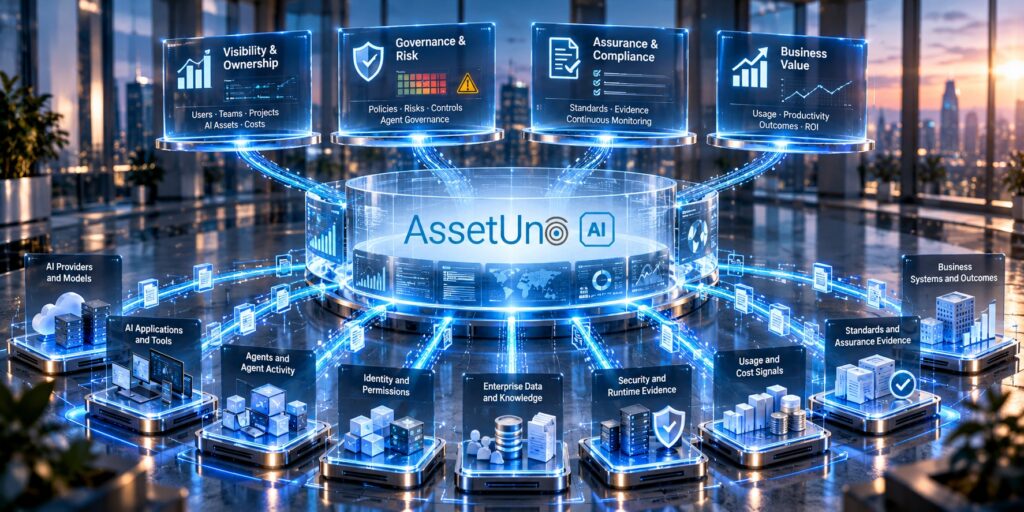
This is the layer AssetUno AI is designed to address.
AssetUno AI does not replace the responsible AI capabilities provided by Microsoft or other AI providers.
It does not replace runtime security controls, identity platforms, AI gateways, DLP systems, model evaluation tools or provider-native monitoring.
Those systems remain important sources of control and evidence.
AssetUno AI creates a provider-independent management and governance layer across them.
The objective is to bring fragmented evidence into a common enterprise context.
That includes several connected capabilities.
AI Discovery and Landscape
Establish which AI providers, services, models, applications and agents are visible across connected sources.
Shadow AI
Identify unmanaged or insufficiently governed AI usage where connected evidence supports discovery and investigation.
Ownership and Organizational Context
Connect AI activity with users, teams, departments, cost centers, projects, repositories and accountable owners.
Agentic AI Governance
Maintain management visibility into agents, executions, tools, actions, provider evidence and connections such as MCP.
Governance and Risk
Connect AI assets and activity with governance requirements, ownership, risk evidence, exceptions and management actions.
Agent Assurance
Evaluate available evidence around autonomy, human oversight, traceability and intervention rather than assuming that an agent is governed simply because it exists in an approved platform.
Compliance and Standards
Connect relevant controls and evidence with frameworks such as ISO/IEC 42001, helping organizations understand what is mapped, what can be evidenced and where gaps remain.
Usage and Cost Optimization
Bring together available license, subscription, token, request, usage and provider cost evidence and connect it with organizational ownership.
AI Value and Outcomes
Move beyond governance activity by connecting AI usage with work output, accepted output and measurable business outcomes.
The distinction is important.
Microsoft can provide deep governance and operational evidence within Microsoft’s AI ecosystem.
Other providers can do the same inside their environments.
AssetUno AI helps the enterprise understand those environments together.
Responsible AI Is Becoming an Operating Model
The most important lesson from Microsoft’s 2026 report is not a particular policy, product or framework.
It is the direction of governance itself.
Responsible AI is becoming continuous.
It is becoming operational.
It is becoming evidence-based.
It is extending from models to applications and agents.
It is connecting development with deployment.
It is connecting policy with engineering.
It is connecting assurance with real-world behavior.
And it increasingly depends on visibility across the entire AI lifecycle.
For enterprises, that means responsible AI maturity cannot be measured only by whether policies exist.
An organization should also be able to answer:
What AI exists across the enterprise?
Who owns it?
Which provider, model or agent is involved?
What risks apply?
What controls and assurance evidence exist?
Where is human oversight required?
What changed after deployment?
What does the AI cost?
And what measurable business outcome does it create?
Responsible AI is no longer only about designing trustworthy technology.
For the enterprise, it is increasingly about maintaining continuous visibility, governance, assurance and accountability across a changing AI environment.
Primary Reference: Microsoft, Responsible AI in 2026: How we are adapting for what’s ahead, September 1, 2026
The article summarizes Microsoft’s 2026 Responsible AI Transparency Report, including its work on adaptive governance, agentic AI, continuous evaluation, observability, assurance, standards and responsible AI deployment.